
Unverified smart contracts were linked to at least $36.7 million in losses across four DeFi exploits over the past six months, as attackers increasingly target protocols whose source code is not publicly available, according to Chainalysis.
The largest incident involved Truebit, which lost $26.2 million after an attacker exploited an integer overflow vulnerability in a contract that had remained unverified on Ethereum since 2021. The other incidents involved Trusted Volumes, Aperture Finance and Ekubo, according to the report.
In each case, the exploited contract had not been verified on a blockchain explorer, meaning its source code was not publicly available for review. According to Chainalysis, that limited scrutiny from security researchers and excluded the contracts from many bug bounty programs despite controlling user funds.
Five protocols saw exploits on unverified smart contracts. Source: Chainalysis
Chainalysis attributed the trend in part to advances in decompilation tools and artificial intelligence, which can help attackers reverse-engineer smart contract bytecode and identify vulnerabilities even when source code is not publicly available. According to the report, what once required “a skilled reverse engineer spending days on a single contract” can now be partially automated across large numbers of unverified contracts.
The report challenges a longstanding assumption in DeFi that keeping smart contract code private provides an additional layer of security. According to Chainalysis, protocols relying on hidden code are increasingly depending on “obscurity as a security measure,” an approach the company said is rapidly losing effectiveness.
Chainalysis recommended source code verification, broader bug bounty coverage and real-time monitoring tools as safeguards against future exploits.
Related: Humanity Protocol token falls 85% amid $30M private key exploit
DeFi security concerns persist after record April losses
The report comes amid a broader rise in crypto exploits. According to DeFiLlama, hackers stole $629.7 million in April alone, the highest monthly total since February 2025.
Two incidents accounted for most of the losses. KelpDAO lost $293 million and Drift Protocol suffered a $280 million exploit, together representing more than 80% of the month’s stolen funds.
Although losses fell sharply in May, with CertiK reporting $68.3 million stolen from cryptocurrency exploits, the fallout from April’s largest attacks continued. In June, blockchain intelligence platform Arkham reported that the attacker behind the KelpDAO exploit had laundered nearly all of the roughly $220 million in unfrozen stolen funds.
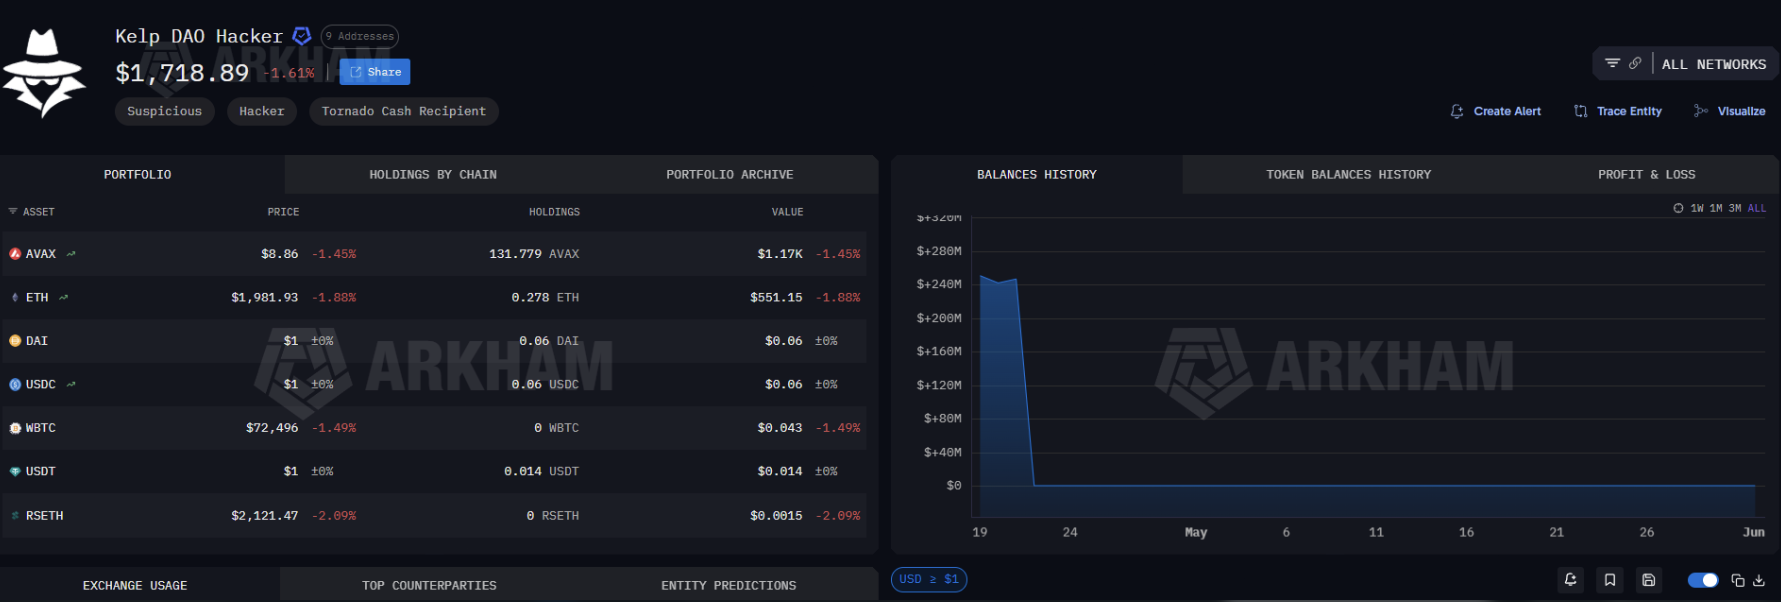
Kelp DAO Hacker-tagged wallet, total balance. Source: Arkham
The KelpDAO exploit also prompted several DeFi protocols to review their security infrastructure, with projects including Solv Protocol announcing plans to migrate to Chainlink’s crosschain infrastructure following internal security reviews.
This month, Anthropic said 560 of the 832 accounts it banned for policy violations over a one-year period had used AI to help prepare cyberattacks, including writing malware and identifying vulnerabilities.
Magazine: The legal battle over who can claim DeFi’s stolen millions